Securing Digital Assets: 2026 Cyber Threat Solutions
Securing Your Digital Assets: Practical Solutions for Protecting Your Online Presence Against 2026’s Evolving Cyber Threats
In an increasingly interconnected world, our lives are intrinsically linked to our digital presence. From personal photos and financial records to business intellectual property and critical infrastructure, our digital assets are invaluable. However, this digital dependency also presents a fertile ground for malicious actors. As we navigate towards 2026, the landscape of cyber threats continues to evolve at an alarming pace, becoming more sophisticated, pervasive, and damaging. Protecting your digital assets is no longer just a best practice; it’s an imperative for survival in the digital age.
The year 2026 promises a new era of technological advancements, but with it comes an equally advanced array of cyber threats. Artificial intelligence (AI) and machine learning (ML), while powerful tools for defense, are also being weaponized by attackers to launch more targeted and evasive assaults. Quantum computing, though still nascent, looms as a potential disruptor to current encryption standards. Furthermore, the proliferation of IoT devices, the expansion of cloud services, and the increasing reliance on remote work models create larger attack surfaces, making the task of securing digital assets more complex than ever.
This comprehensive guide delves into the practical solutions and proactive strategies necessary to safeguard your digital assets against the sophisticated cyber threats projected for 2026. We will explore cutting-edge technologies, robust security frameworks, and essential human-centric approaches to build a resilient defense. Our goal is to equip you with the knowledge and tools to not only react to threats but to anticipate and mitigate them effectively, ensuring the integrity, confidentiality, and availability of your invaluable digital presence.
Understanding the Evolving Threat Landscape for Digital Asset Security in 2026
Before we can effectively protect our digital assets, we must first understand the nature of the threats we face. The cyber threat landscape is a dynamic ecosystem, constantly shifting with technological advancements and geopolitical developments. In 2026, we can expect several key trends to dominate the cybersecurity narrative, demanding a proactive and adaptive approach to digital asset security.
AI-Powered Attacks and Defenses
The dual nature of AI is perhaps the most significant factor shaping the 2026 threat landscape. While AI and ML are invaluable for threat detection, anomaly identification, and automating security responses, they are also being leveraged by attackers. AI-powered phishing campaigns are becoming increasingly convincing, capable of crafting highly personalized and contextually relevant messages that bypass traditional filters. Adversarial AI can be used to bypass security systems, generate polymorphic malware that evades detection, and even automate reconnaissance and exploitation phases of an attack. This necessitates a shift towards AI-driven defenses that can learn and adapt as quickly as the threats they are designed to counter.
Sophisticated Ransomware and Extortion Tactics
Ransomware attacks have been a persistent menace, and in 2026, they will likely become even more sophisticated. Expect multi-layered extortion tactics where attackers not only encrypt data but also exfiltrate it, threatening to leak sensitive information if the ransom is not paid. Supply chain attacks will continue to be a favored vector, allowing attackers to compromise multiple organizations through a single breach point. The focus will shift from mere data recovery to preventing data exfiltration and reputational damage, making robust data loss prevention (DLP) and incident response plans critical components of digital asset security.
The Rise of Quantum Computing Threats
While full-scale quantum computers capable of breaking current encryption standards are still a few years away, the potential threat they pose to our digital assets cannot be ignored. Cryptographic agility, the ability to switch between cryptographic algorithms quickly and efficiently, will become paramount. Organizations need to start exploring post-quantum cryptography (PQC) solutions and developing migration strategies to ensure their long-term digital asset security. Proactive research and development in this area will be crucial to avoid a future ‘crypto-apocalypse’.
IoT Vulnerabilities and Edge Computing Risks
The proliferation of Internet of Things (IoT) devices, from smart home gadgets to industrial sensors, expands the attack surface exponentially. Many IoT devices are deployed with weak security defaults, making them easy targets for botnets and distributed denial-of-service (DDoS) attacks. As edge computing gains traction, processing data closer to its source, the security of these distributed environments becomes a significant concern for digital asset security. Securing every endpoint, implementing strong authentication, and ensuring regular patching for IoT devices will be vital.
Human Element: The Weakest Link and Strongest Defense
Despite technological advancements, the human element remains a primary vulnerability. Social engineering tactics, phishing, and insider threats continue to be effective methods for gaining unauthorized access to digital assets. However, humans can also be the strongest line of defense. Comprehensive security awareness training, fostering a culture of cybersecurity, and implementing robust access controls are essential for mitigating human-centric risks and strengthening overall digital asset security.
Pillars of Proactive Digital Asset Security for 2026
Building a resilient defense against the complex threats of 2026 requires a multi-faceted approach. Here, we outline the foundational pillars that will underpin effective digital asset security strategies.
1. Advanced Encryption and Cryptographic Agility
Encryption is the bedrock of data protection. In 2026, merely encrypting data will not suffice; the focus must shift to advanced and adaptive encryption methods. Utilize end-to-end encryption for all sensitive communications and data at rest and in transit. Explore homomorphic encryption, which allows computation on encrypted data without decrypting it, offering a new layer of privacy and security, especially in cloud environments. As mentioned, cryptographic agility is critical. Organizations should have a clear strategy for migrating to post-quantum cryptography (PQC) algorithms as they mature and become standardized. This involves inventorying current cryptographic usage, assessing risks, and planning for seamless transitions to quantum-resistant solutions to protect long-term digital asset security.
2. AI-Driven Threat Detection and Response
Traditional signature-based security systems are increasingly ineffective against polymorphic and AI-generated malware. AI and ML are indispensable for proactive threat detection and rapid response. Implement AI-powered Security Information and Event Management (SIEM) and Extended Detection and Response (XDR) platforms that can analyze vast amounts of data, identify anomalous behavior, predict potential attacks, and automate response actions. These systems can detect subtle indicators of compromise that human analysts might miss, significantly reducing the dwell time of attackers and minimizing damage to digital assets. Machine learning models can be trained to recognize novel attack patterns, adapt to new threats, and even identify zero-day vulnerabilities more effectively.
3. Robust Identity and Access Management (IAM)
Identity is the new perimeter. Strong IAM solutions are fundamental to securing digital assets. Implement multi-factor authentication (MFA) or, even better, passwordless authentication across all systems. Adopt Zero Trust Network Access (ZTNA) principles, where no user or device is inherently trusted, and access is granted only after rigorous verification. This involves continuous authentication and authorization based on context, device posture, and user behavior. Privileged Access Management (PAM) solutions are also crucial to control, monitor, and audit access to critical systems and sensitive digital assets, preventing insider threats and lateral movement by external attackers.
4. Cloud Security Posture Management (CSPM) and Cloud Workload Protection Platforms (CWPP)
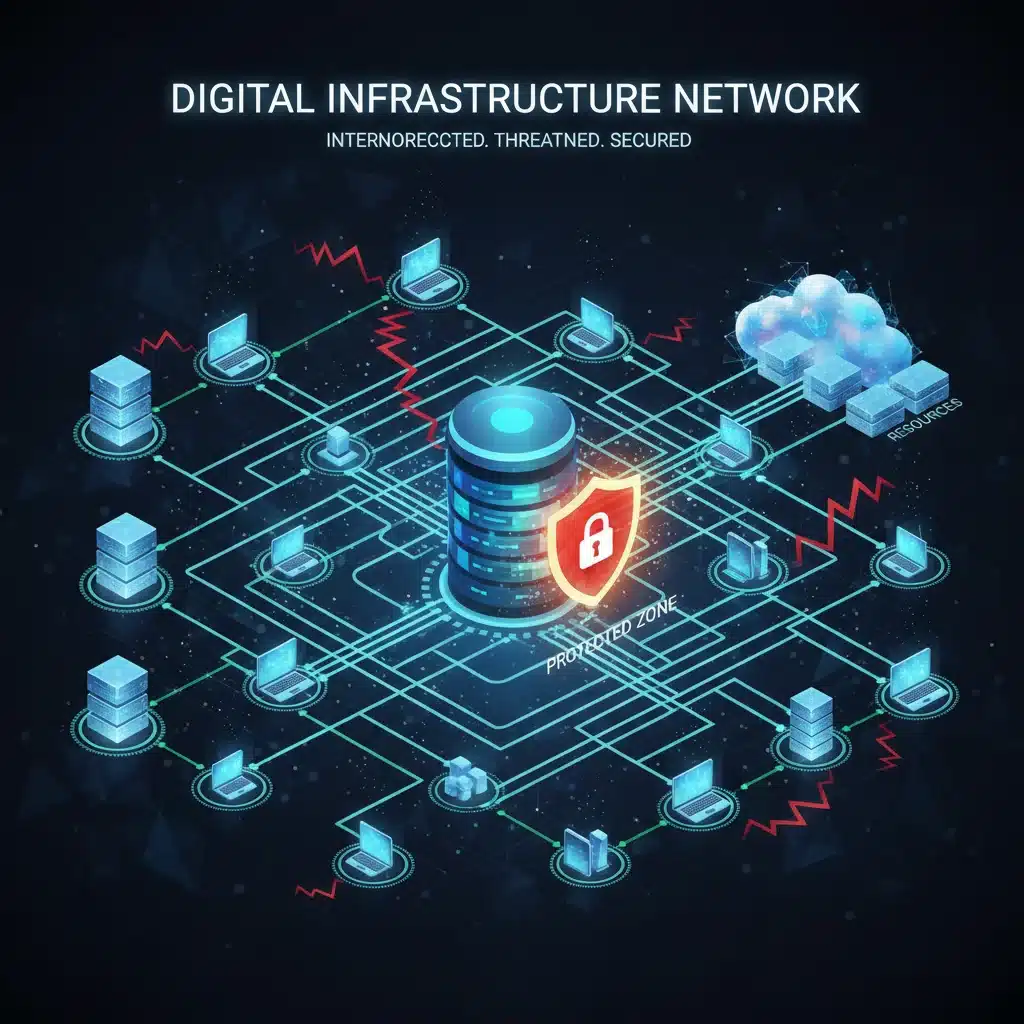
As organizations increasingly leverage cloud services, securing these environments becomes paramount for digital asset security. Misconfigurations in cloud infrastructure are a leading cause of data breaches. CSPM tools continuously monitor cloud environments for security misconfigurations, compliance violations, and policy deviations, providing actionable insights for remediation. CWPP solutions protect workloads (virtual machines, containers, serverless functions) running in the cloud from various threats, offering capabilities like vulnerability management, runtime protection, and host-based intrusion prevention. A unified cloud security strategy that integrates these tools is essential to protect digital assets residing in hybrid and multi-cloud architectures.
5. Data Loss Prevention (DLP) and Data Classification
Knowing where your sensitive digital assets reside and controlling their movement is critical. Implement robust DLP solutions that can identify, monitor, and protect sensitive data whether it’s in use, in motion, or at rest. This requires a comprehensive data classification strategy, categorizing data based on its sensitivity and regulatory requirements. DLP policies should be enforced across endpoints, networks, and cloud applications to prevent unauthorized data exfiltration, ensuring compliance and safeguarding intellectual property. As ransomware attackers increasingly resort to data exfiltration, effective DLP becomes a non-negotiable component of digital asset security.
6. Security Awareness Training and Human Firewall
Technology alone cannot fully protect digital assets. Employees are often the first line of defense, and unfortunately, also the most common entry point for attackers. Regular, engaging, and relevant security awareness training is crucial. This training should cover topics like phishing detection, social engineering tactics, strong password practices (or better yet, passwordless authentication adoption), and safe browsing habits. Foster a culture where cybersecurity is everyone’s responsibility, encouraging employees to report suspicious activities without fear of reprisal. A well-informed human firewall significantly enhances overall digital asset security.
Emerging Technologies and Future-Proofing Digital Asset Security
Beyond the fundamental pillars, several emerging technologies and strategic approaches will play a crucial role in future-proofing digital asset security against the threats of 2026 and beyond.
Zero Trust Architecture (ZTA)
Zero Trust is not a single technology but a security philosophy that assumes no user, device, or network inside or outside an organization should be trusted by default. Every access request to digital assets must be authenticated, authorized, and continuously validated. Implementing ZTA involves micro-segmentation, least privilege access, continuous monitoring, and strict control over data flows. This model significantly reduces the impact of breaches by limiting lateral movement within networks, making it a cornerstone of modern digital asset security.
Blockchain for Enhanced Security and Integrity
While often associated with cryptocurrencies, blockchain technology offers significant potential for enhancing digital asset security. Its decentralized and immutable ledger can be used for secure identity management, verifiable data integrity, and transparent audit trails. For instance, blockchain can secure supply chain data, verify software updates, or create tamper-proof records of critical transactions. As the technology matures, expect to see more innovative applications of blockchain in securing various types of digital assets.
Cybersecurity Mesh Architecture (CSMA)
Gartner predicts that by 2024, organizations adopting a cybersecurity mesh architecture will reduce the financial impact of security incidents by an average of 90%. CSMA is a distributed architectural approach that provides a composable, scalable, and interoperable security posture. Instead of a perimeter-centric model, CSMA focuses on securing individual access points, assets, and identities, regardless of their location. This approach is particularly effective for protecting digital assets in complex, hybrid environments, offering consistent security policies and centralized management across diverse security tools.
Security Chaos Engineering
Inspired by chaos engineering in software development, security chaos engineering involves intentionally injecting failures or attacks into systems to identify weaknesses and improve resilience. By simulating realistic cyberattacks in a controlled environment, organizations can proactively discover vulnerabilities in their digital asset security posture, test incident response plans, and strengthen their defenses before real attackers exploit them. This proactive testing fosters a more robust and adaptable security framework.
Practical Steps for Implementing Robust Digital Asset Security
Transitioning from theory to practice requires concrete steps. Here’s a roadmap for implementing and maintaining strong digital asset security.
1. Conduct Regular Risk Assessments and Vulnerability Scans
Understanding your attack surface and identifying potential weaknesses is the first step. Regularly perform comprehensive risk assessments to identify critical digital assets, potential threats, and existing vulnerabilities. Conduct frequent vulnerability scans and penetration testing to uncover exploitable flaws in your systems, applications, and network infrastructure. Prioritize remediation based on the severity of the identified risks and the value of the affected digital assets.
2. Develop and Practice an Incident Response Plan
No security measure is foolproof. A well-defined and regularly practiced incident response plan is crucial for minimizing the impact of a breach. This plan should detail steps for detection, containment, eradication, recovery, and post-incident analysis. Include roles and responsibilities, communication protocols, and legal/regulatory considerations. Regular tabletop exercises and simulations will ensure that your team is prepared to act swiftly and decisively when a security incident threatens your digital assets.
3. Implement Strong Data Backup and Recovery Strategies
In the face of ransomware and data corruption, reliable backups are your last line of defense. Implement a robust 3-2-1 backup strategy: three copies of your data, on two different media, with one copy offsite. Ensure that backups are immutable, regularly tested for recoverability, and isolated from your primary network to prevent them from being compromised during an attack. This ensures business continuity and the ability to restore your digital assets even after a catastrophic event.
4. Patch Management and Configuration Hardening
Unpatched software and misconfigured systems are prime targets for attackers. Establish a rigorous patch management program to ensure all operating systems, applications, and firmware are updated promptly. Implement configuration hardening guidelines, removing unnecessary services, closing unused ports, and applying secure configurations to all devices and systems. Continuous monitoring for configuration drift is also important to maintain a secure baseline for your digital assets.
5. Vendor Security Assessment and Third-Party Risk Management
Your security posture is only as strong as your weakest link, and often that link is a third-party vendor. Conduct thorough security assessments of all third-party suppliers, cloud providers, and partners who have access to your digital assets. Establish clear security clauses in contracts, conduct regular audits, and monitor their security practices to mitigate supply chain risks. A comprehensive third-party risk management program is essential for protecting your extended digital ecosystem.
6. Embrace a DevSecOps Culture
Integrate security into every stage of the software development lifecycle (SDLC) by adopting a DevSecOps approach. This means security is not an afterthought but is woven into the design, development, testing, and deployment phases. Automated security testing, static and dynamic application security testing (SAST/DAST), and continuous security monitoring help identify and remediate vulnerabilities early, ensuring that applications and the digital assets they manage are secure by design.
Conclusion: A Continuous Journey for Digital Asset Security
Securing your digital assets in 2026 and beyond is not a one-time project but a continuous journey. The cyber threat landscape is constantly evolving, requiring organizations and individuals to be vigilant, adaptable, and proactive. By embracing advanced encryption, AI-driven defenses, robust identity management, and a comprehensive security culture, you can build a formidable shield around your invaluable digital presence.
The convergence of sophisticated AI-powered attacks, the looming threat of quantum computing, and the expanding attack surface demand a strategic and layered defense. Investing in leading-edge security technologies, fostering a cybersecurity-aware workforce, and implementing agile security frameworks like Zero Trust and Cybersecurity Mesh Architecture will be paramount. Remember that every click, every device, and every data point represents a potential vulnerability or an opportunity to strengthen your defenses.
The future of our digital lives depends on our collective commitment to strong digital asset security. By staying informed, continuously adapting our strategies, and leveraging the best available tools, we can navigate the challenges of 2026 and ensure a secure and thriving digital future for all.